Phishing is no longer full of mistakes
Fraudulent messages can now look like ordinary communication from a colleague, supplier, bank or company management. Employees learn to spot warning signs even when an attack looks convincing.

Most attacks do not start by breaking through technology, but with a convincing email, a weak password or a carelessly shared file. We teach your employees to recognise risky situations and respond appropriately, clearly, practically and without unnecessary scare tactics.
Attackers know that the easiest way into a company is often through a person rather than technology. They exploit stress, time pressure, trust and everyday working habits. Yet employees do not need to be security specialists to assess most of these situations correctly.
Fraudulent messages can now look like ordinary communication from a colleague, supplier, bank or company management. Employees learn to spot warning signs even when an attack looks convincing.
Weak, reused or improperly stored passwords make it easier for attackers to access company accounts. We show participants how to protect their logins without unnecessarily complicated rules.
Misconfigured sharing, a public link or a personal device can expose sensitive information to people who should not see it.
An attack can arrive through a mobile phone, social network, fake online shop, QR code or fraudulent payment. That is why the training uses situations employees actually encounter.
New employees arrive with different experience and working habits. The training helps companies establish consistent ground rules for safe behaviour during onboarding and reduces the risk of newcomers bringing unsuitable practices from their previous workplace.
They will be able to identify typical signs of phishing, manipulation and other scams, in email and beyond.
← BackThey will understand how to use passwords, password managers and multi-factor authentication, and why a password alone may not be enough.
← BackThey will learn to share files correctly, use cloud services and check who retains access.
← BackThey will not have to guess what to do with a suspicious message, an unexpected request or a possible incident.
← BackThe training is designed for everyday users across the company. Participants do not need technical knowledge or previous cybersecurity experience.
We tailor the depth and emphasis of individual topics to your company's environment, industry and internal policies.
The training takes place in person and builds on situations participants know from work and personal life. We support the explanations throughout with practical examples, exercises and group discussion.
Participants do more than listen passively. They work through scenarios, answer questions and assess risky situations together.
← BackParticipants practise selected topics using concrete examples. This helps them remember the steps they can use later.
← BackWe explain security through situations that can actually happen: a suspicious email, an unexpected payment request, a fake login page or an improperly shared document.
← BackThe training includes time for participants' experiences, questions and situations specific to their work. A dedicated question-and-answer session follows at the end.
← BackThe length of the training depends on group size, the desired depth of individual topics and the time allocated to practical exercises and discussion. These are not two fixed, separate options, we prepare a scope that fits each company's needs.
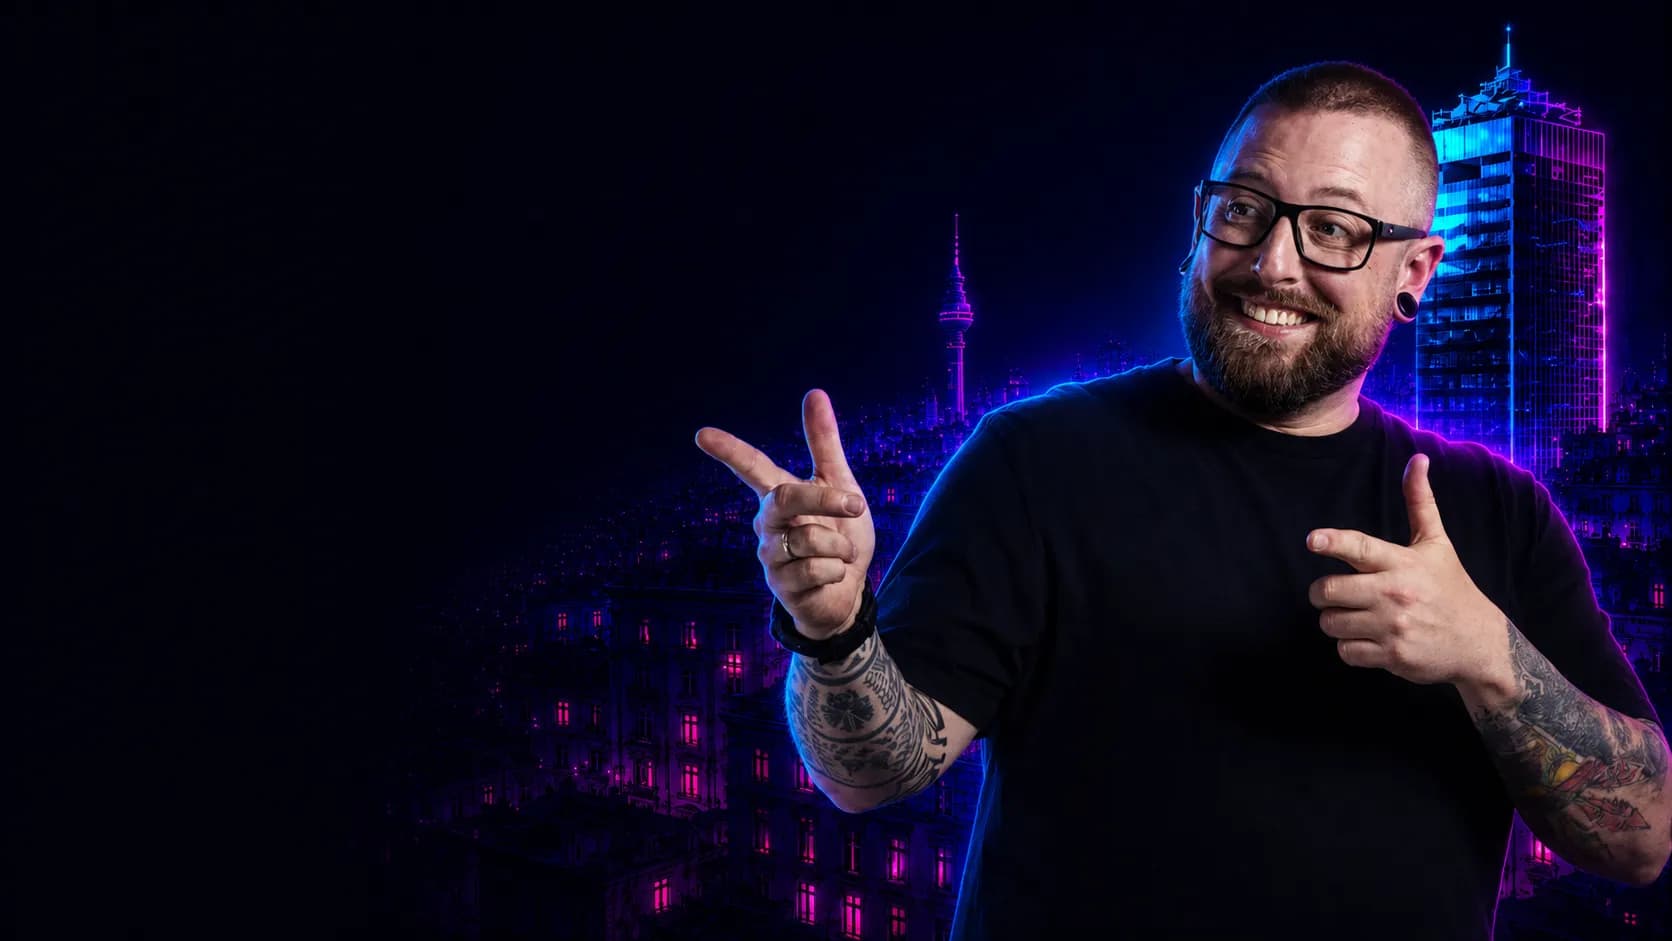
Pavel “Spajk” Matějíček is a cybersecurity trainer and consultant at BOIT. He has worked in cybersecurity for over 10 years, focusing on user security awareness, social engineering prevention and practical protection of company data in everyday operations. Previously, he worked at ESET, helping educate people about cyber threats.
In his training, he explains things clearly, without unnecessary technical jargon, using real-world situations. He shows participants how attackers think, the techniques they use and how to defend against them effectively in everyday work.
Participants work with examples they may encounter in email, on the phone and during an ordinary working day.
No technical knowledge is required. We turn complex principles into simple decisions and useful habits.
Before the training, we take into account your industry, internal policies, typical work situations and participants' knowledge.
Discussion and Q&A are more than extras. They help apply general recommendations to your company's specific environment.
Pavel's cybersecurity training has the pace of an ice hockey game: fast, practical and full of involvement. Participants aren't spectators: they're active players. No boredom, just clear insights they can use straight away.
Accolade has worked with Pavel for several years. His proactive approach makes his training one of our most popular and best-attended sessions, engaging people across generations.
We've worked with BOIT on information security talks for a long time. Pavel combines excellent expertise with an entertaining style. In over 10 years of organising specialist events, BOIT has been one of our best partners. Highly recommended.
No. The training is designed for everyday users and does not require technical education or cybersecurity experience.
The recommended group size is 5 to 30 participants. This allows active participation, practical exercises, discussion and plenty of room for questions.
We determine the exact length based on group size, the desired depth of topics and the time allocated to exercises and discussion. These are not two fixed programme options.
Yes. We can adapt the content to your industry, work situations, internal policies and security priorities.
We offer this training in person. Face-to-face delivery allows better participant involvement, practical exercises and responses to the group's questions.
The training includes a presentation, handbook, checklist, learning materials and certificate.
Yes. Questions and discussion are part of the entire programme, with dedicated Q&A time at the end.
Yes. Companies often include the training in new employee induction. It helps establish safe working habits from the start and introduces employees to the basic rules for handling accounts, emails, devices and company data. We can tailor the content to your company's internal policies and typical situations.
Prices start at CZK 45,000. The final quote depends on the duration, depth of content and number of participants.