One prompt can leak sensitive data
A contract, client data or an internal document can end up in a public AI service before the user realises the consequences.

Artificial intelligence is already an everyday work tool, and a new security risk. This course explains how AI really works, what you can share with it, how to verify its output and how to set rules that protect data, employees and your organisation.
Without shared rules, each employee decides which tool to use, what data to share and whether its output can be trusted.
A contract, client data or an internal document can end up in a public AI service before the user realises the consequences.
Hallucinations, bias and missing context can produce confident answers that lead to poor decisions.
The difference between safe and risky use cannot be left to individual intuition alone.
AI accelerates phishing, social engineering, deepfakes and the creation of convincing scams.
Distinguish between public and enterprise AI services and understand why their terms and data handling differ.
← BackLearn to classify and anonymise data and decide what should never go into an AI tool.
← BackLook beyond confident wording and use checks proportionate to the consequences of the result.
← BackUnderstand deepfakes, voice cloning, prompt injection and how AI changes phishing and fraud.
← BackThe course connects practical AI use with security, accountability and company policy. No technical background is required.
We adjust the emphasis to your tools, participants' roles, types of data and whether your organisation already has an AI policy.
Explanations are supported by practical scenarios, examples of safe and risky inputs, and current attacks using generative AI.
Participants learn AI principles and limitations without needing programming or data science knowledge.
← BackWe show where AI genuinely helps and where its use creates disproportionate risk.
← BackConcrete examples show effective prompts, inappropriate inputs and ways to anonymise data.
← BackWe connect deepfakes, prompt injection and AI phishing to measures an organisation can actually implement.
← BackWe adapt the content to your AI services, participants' roles, internal data classification and the maturity of your AI policy.
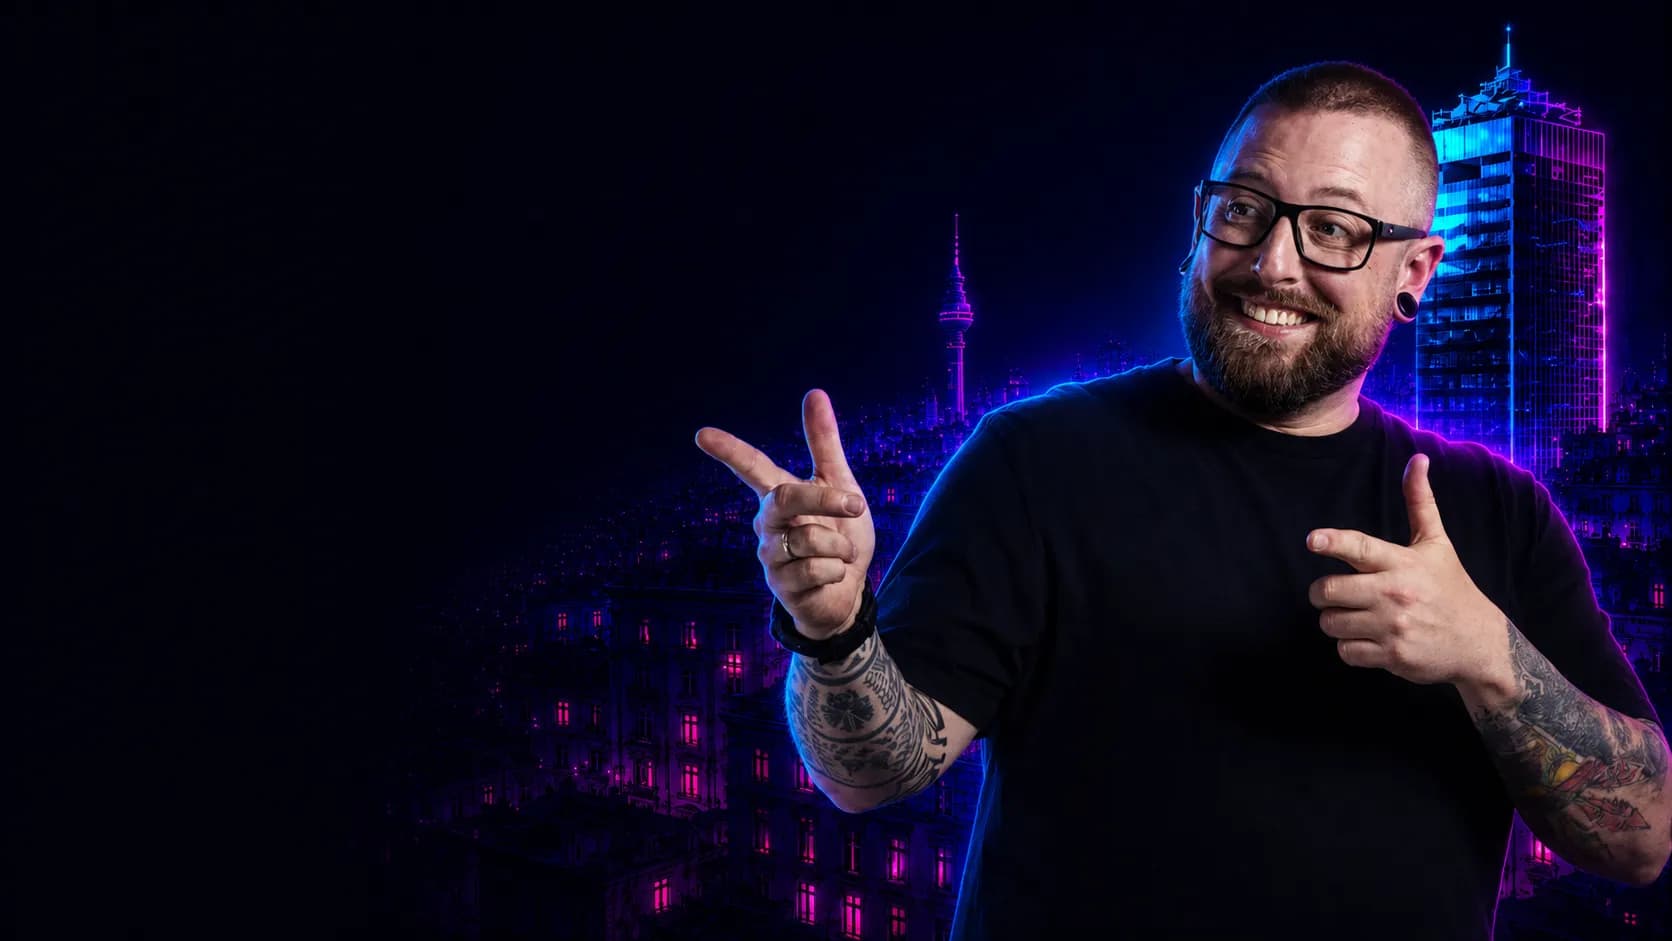
Pavel “Spajk” Matějíček is a cybersecurity trainer and consultant at BOIT. He has worked in cybersecurity for over 10 years, focusing on user security awareness, social engineering prevention and practical protection of company data in everyday operations. Previously, he worked at ESET, helping educate people about cyber threats.
In his training, he explains things clearly, without unnecessary technical jargon, using real-world situations. He shows participants how to use technology effectively, where risks arise and how to put defences into practice at work.
We don't ban a useful tool. We show how to benefit from it without unnecessary risk.
We translate general principles into the prompts, data and decisions employees encounter.
An AI policy only works when people understand its boundaries and can apply them in everyday work.
We account for your tools, data types, internal rules and participants' specific roles.
Pavel's cybersecurity training has the pace of an ice hockey game: fast, practical and full of involvement. Participants aren't spectators: they're active players. No boredom, just clear insights they can use straight away.
Accolade has worked with Pavel for several years. His proactive approach makes his training one of our most popular and best-attended sessions, engaging people across generations.
We've worked with BOIT on information security talks for a long time. Pavel combines excellent expertise with an entertaining style. In over 10 years of organising specialist events, BOIT has been one of our best partners. Highly recommended.
No. It is designed for employees, management and teams that set company policies. We explain the technical principles without unnecessary jargon.
No. We start with how AI works, then move on to practical use, risks and protection.
Yes. We explain the differences between public and enterprise services and tailor the examples to the tools used in your organisation.
The training explains the principles, roles and boundaries of an effective AI policy. It does not replace legal services or the separate preparation of internal documentation.
Yes. Participants gain a practical understanding of the relevant legal framework and its impact on AI use within the organisation.
We offer this training in person. The face-to-face format allows for live demonstrations, group scenarios and discussion.
The training lasts 3 to 4 hours, with prices starting at CZK 45,000. The final quote depends on the scope and level of customisation.